For MSPs and internal IT
Server and network management.
Manage servers and networks with agentic workflows. Your agent investigates and plans; your team reviews, approves, and controls execution.
RealmHelm / Operations dashboard

Health and alerts
See failed collections, device health issues, and pending approvals. Check which devices have monitoring configured.
Device inventory
Import from PRTG, Active Directory, and discovery. Review duplicates and organize devices by location and importance.
Policy compliance
Audit configurations against your own rules. Track findings and exceptions, then review the proposed fixes.
Agentic IT management
Agentic workflows.
Human control.
Your agent queries RealmHelm for devices, connections, configurations, and operational history, then builds change manifests from that context.
RealmHelm turns those manifests into plans your team can review, approve, and control.

Investigate
Give your agent device details, topology, interface usage, and configuration history to plan the work.
Review
Inspect targets, commands, checks, and rollback. Approve device changes in the web UI.
Control
Follow results. Pause, retry, or stop execution. Request rollback where supported.
Custom policies and remediation
Audit configurations
against your own policies.
Define the standards your customers and teams work to. Apply them to the right servers and network devices, and see where configurations fall short.

Define and test rules
Build custom validation rules, test them against collected device data, and group them into policies scoped by location or device criteria.
Track findings and exceptions
Inspect results by device and rule. Follow compliance history and record exceptions with expiry and review dates.
Review and run fixes
Attach remediation rules to propose fixes. Review each device’s commands, approve in the browser, and inspect the execution results.
Server management
Windows Server
and Ubuntu.
Check what’s installed, which services were discovered, and how each host is configured.
- Software, services, and certificatesReview OS and package versions, services, and TLS certificates. Match captured software against vulnerability findings.
- Review remediation commandsRead the proposed commands for a non-compliant host, approve them in the browser, and check the result for each device.
- Physical and virtual inventoryIdentify physical and virtual hosts. Collect inventory from vCenter and its ESXi hosts; inspect server controllers through Redfish.

Network management
Configuration backups
and controlled changes.
Back up configurations, investigate faults, and plan firmware upgrades on supported platforms. EOS, IOS XE, and FortiOS configuration changes can carry rollback timers.
- Configuration historySchedule backups, compare each configuration with its preceding version, and see the compliance impact. Search current device configurations.
- Network investigationTrace an IP or MAC address to a switch port and VLAN. Inspect BGP and OSPF routes through a site agent that peers with your routers.
- Firmware upgradesSet targets by model and deploy in waves. Site agents serve verified images; disruptive work reserves known HA or MLAG peers.
- Health monitoringUse SNMP and ping, with ready-made checks for UPS units, hardware sensors, and Cisco fans, power, and temperature.

Security and access
Find the devices
that need a fix.
Match captured software against the NetPrecedent vulnerability feed. Findings are grouped by fix and ranked Act, Attend, or Track using known-exploited and exploit-likelihood signals.
Open a finding to see the affected devices. Get an email when new exposure is detected.

Network access and administrator logins
Manage RADIUS and TACACS+ authorization profiles. Inspect sessions and audit logs for network access and device administration.
Configuration assistance
Use your Anthropic account to summarize configuration changes and draft compliance rules.
Operational reporting
Schedule the reports
your team needs.
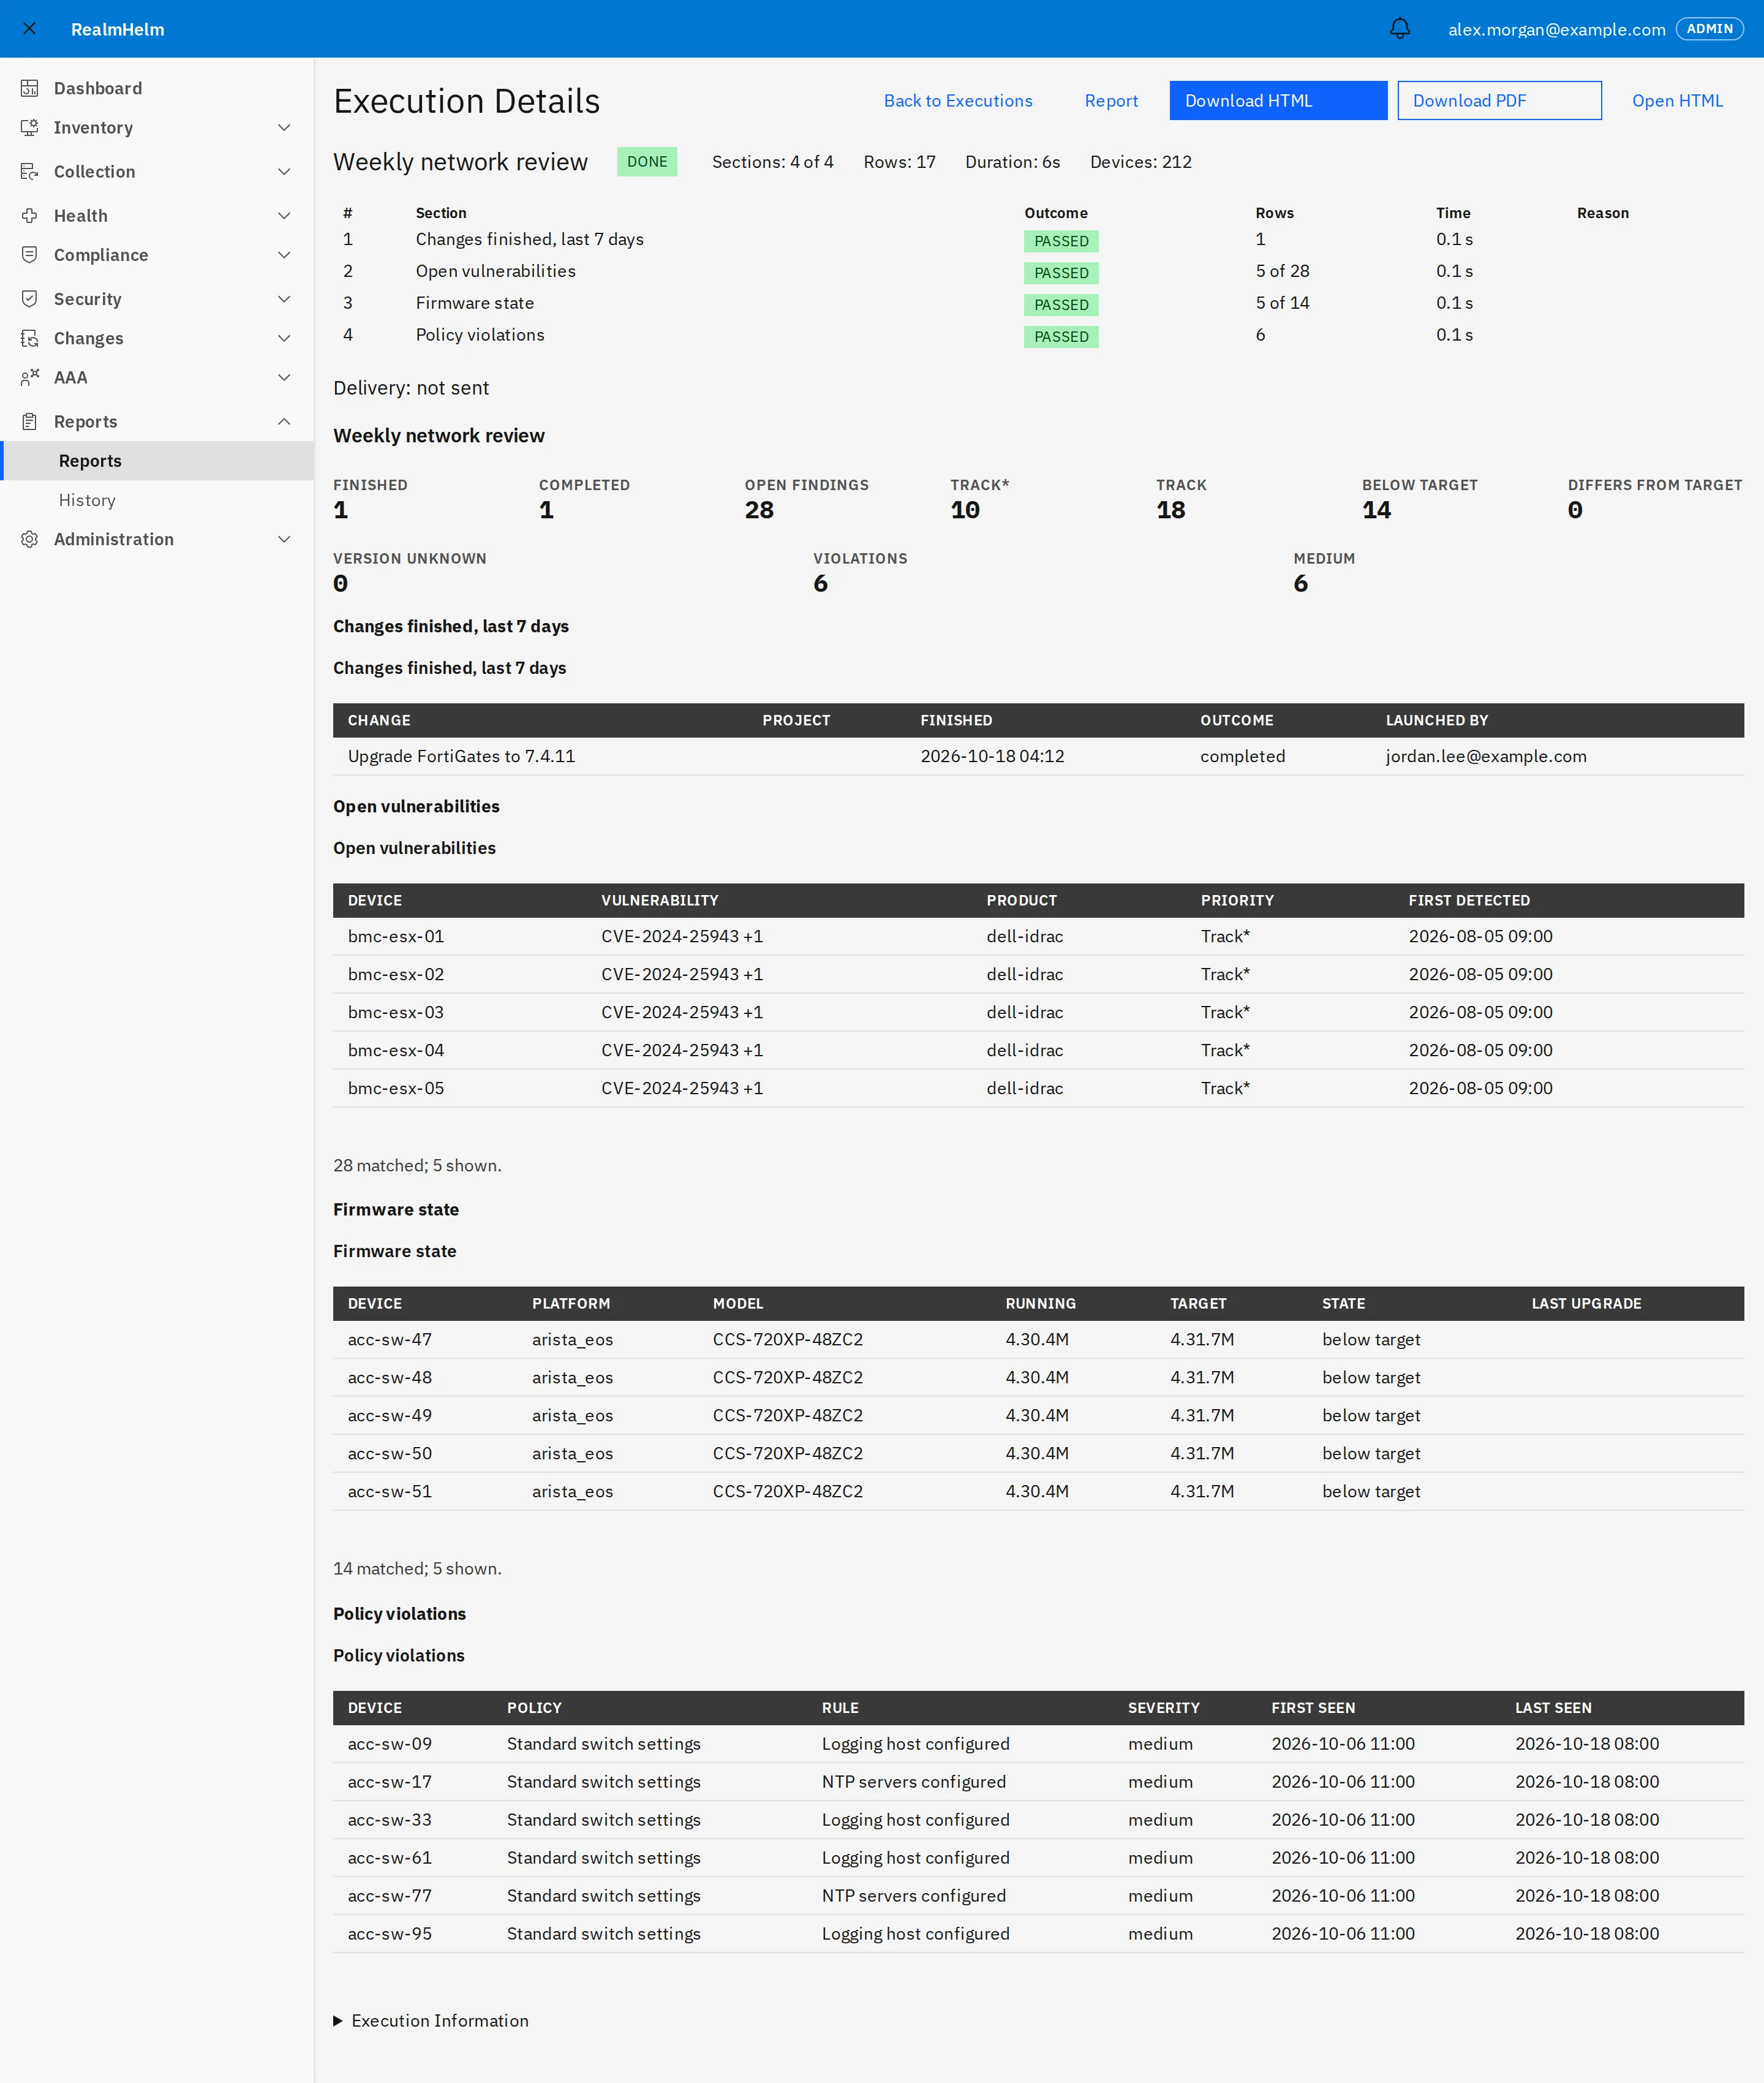
Choose device groups and report sections, then set an email schedule. Include inventory, availability, health, vulnerabilities, compliance, and firmware or configuration changes.
Deployment
Host in your Azure
subscription, or ours.
Deploy RealmHelm in your own Azure subscription through our Azure Marketplace offer. Or choose a dedicated instance hosted by NetPrecedent.
Site agents connect outbound over HTTPS; no site VPN or inbound internet ports are needed.
ONE CUSTOMER ENVIRONMENT
RealmHelm applianceYour Azure subscription or NetPrecedent hostingServers and network devices
Servers and network devices
Microsoft Entra ID
Sign in with Admin, Operator, and Read-only roles.
Credentials in Azure Key Vault
Device and server credentials are fetched for each run.
Appliance protection
Signed appliance updates and a web application firewall.
Supported platforms
Check support for your equipment. Monitoring includes availability checks; configuration changes and firmware upgrades vary by platform.
Scroll sideways to compare all capabilities →
| Network platform | Backups | Monitoring | Changes | Firmware |
|---|---|---|---|---|
| Arista EOS | ✓ yes | ✓ yes | ✓ yes | ✓ yes |
| Cisco IOS and IOS XE | ✓ yes | ✓ yes | ✓ yes | ✓ yes |
| Cisco NX-OS | ✓ yes | ✓ yes | ✓ yes | ✓ yes |
| Fortinet FortiOS | ✓ yes | ✓ yes | ✓ yes | ✓ yes |
| Cisco IOS XR | ✓ yes | ✓ yes | – no | – no |
| Dell OS9 | ✓ yes | ✓ yes | – no | – no |
| Cradlepoint, through NCM | – no | ✓ yes | – no | – no |
| Siklu EtherHaul | ✓ yes | ✓ yes | – no | – no |
| Ubiquiti airFiber | ✓ yes | ✓ yes | – no | – no |
Servers: Windows Server and Ubuntu. VMware vCenter and its ESXi hosts for inventory and captured state.
Server controllers: Redfish, including Dell iDRAC, HPE iLO, Supermicro, and Lenovo XClarity.
Cameras and other equipment: Milestone XProtect camera inventory and image checks. Monitoring for devices that answer SNMP or ping.
Inventory sources: PRTG, Active Directory, Milestone XProtect, Cradlepoint NCM, network scans, and CSV imports.
Talk to NetPrecedent
See RealmHelm on a call.
Tell us what you manage. We’ll walk through the server and network workflows relevant to your team.