
Security and compliance
Configuration assessments, vulnerability exposure and TLS scans, with findings tied to device evidence.
Configuration compliance
Assess stored captures against supported DISA STIG benchmarks and your own rules. Review the configuration lines judged by each check.
Record exceptions, attach manual attestations and prepare fixes with verification on the change engine.
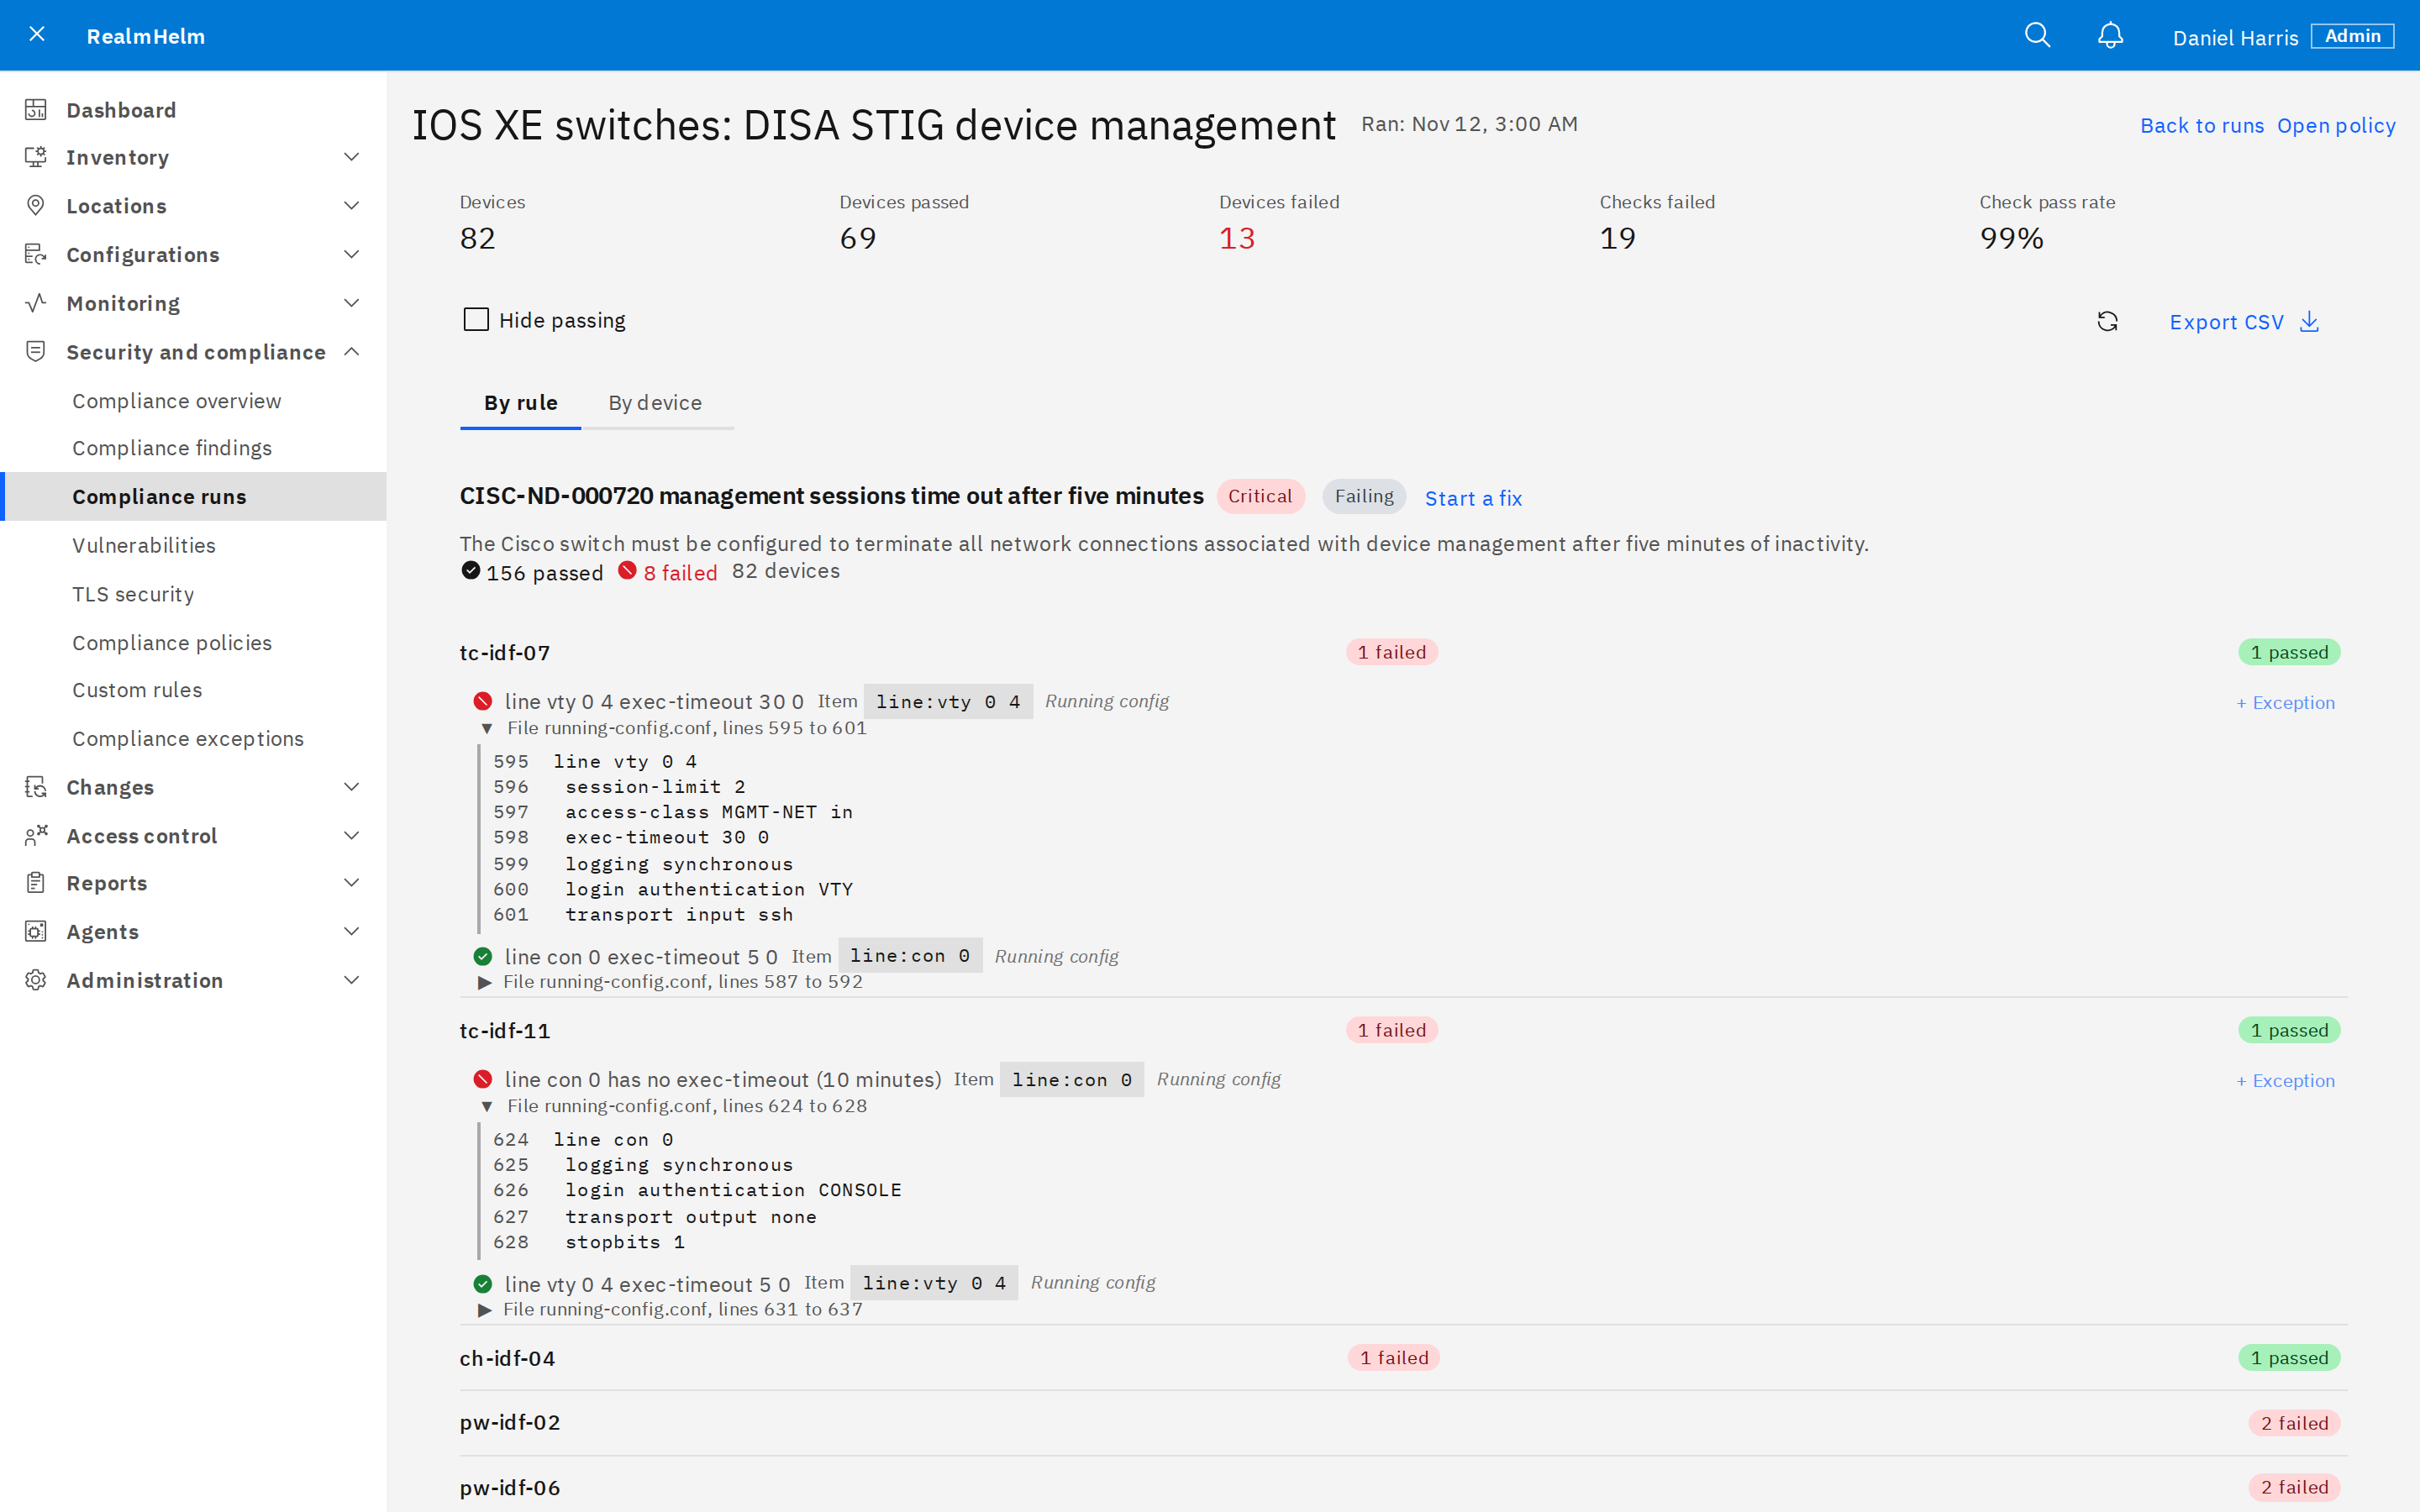
- Deterministic evaluation
- Rules evaluate stored evidence.
- Custom rules
- Write rules through rhctl or use a configured Anthropic connector to draft them and test them with examples.
- Standards mapping
- Built-in STIG content maps to NIST SP 800-53 Rev 5 through CCI references.
Vulnerability exposure
Match reported models and versions against signed vulnerability content from NetPrecedent.
Where supported, use captured configuration to distinguish exposed, not exposed and unchecked devices. Review priority signals, record accepted risk or false positives and open affected devices for a firmware upgrade.
Firmware upgradesTLS service checks
Run TLS scans from site agents against discovered services or specified names. Review grades, certificate expiry and exceptions.
Certificate renewal can be handled separately through a change or runbook.
See it in RealmHelm
Talk with an engineer about your equipment and the work you need to do.